Korff on Kuner: Schrems II Re-Examined
Comments on: Chris Kuner, Verfassungsblog, Schrems II Re-Examined, 25 August 2020: Below are some comments by me on the above blog.
Continue readingData protection and digital competition
by Ian Brown, Douwe Korff and friends
Comments on: Chris Kuner, Verfassungsblog, Schrems II Re-Examined, 25 August 2020: Below are some comments by me on the above blog.
Continue reading
States should not be allowed to hide behind asserted independence of state organs. They must reply in substance to serious allegations, including that the supposedly independent state organs are applying the law in an excessive and repressive manner that threatens fundamental rights.
Continue reading
This Note is an immediate response to the recent EDPB guidance relating to the processing of certain special categories of personal data that enjoy special protection under the GDPR, commonly referred to as “sensitive data”. The Note explains why the EDPB’s guidance is not clear enough.
Continue reading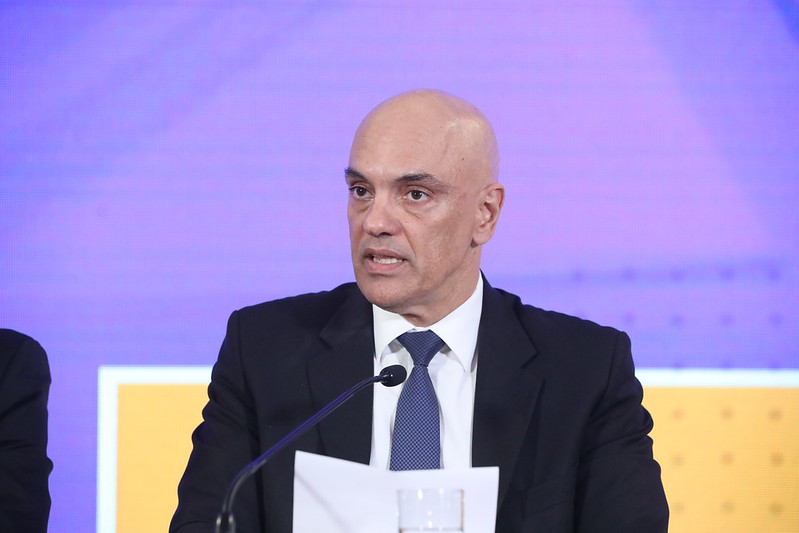
Brazilian supreme court justice Alexandre de Moraes’ sweeping order last night blocking access to X/Twitter is a foretaste of action by other courts and governments around the world. They will no doubt be watching closely.
Continue reading
This analysis explains why the EU bans on Russian media outlets, and the Court of Justice judgment in RT France v. Council relating to them, are wrong. The bans limit the right of individuals in the EU to receive such information and ideas, while EU rules on sanction violations can easily lead to the use of the criminal law against individuals in the EU for non-violent political speech.
Continue reading
As well as the Belgian Data Protection Authority decision I criticised earlier this week, it appears the French DPA has issued similar guidance on the use of personal data to train AI models. My detailed analysis below shows that, in relation to purpose-specific AI systems, it makes no sense: the training of the system cannot be separated from the ultimate purpose of the system. This has a major bearing on the issue of compatibility.
Continue reading
On 15 March, the Belgian Data Protection Authority issued a decision under the GDPR on the use, by a bank, of the transaction data of its customers to build direct marketing data models. This analysis shows why that decision was fundamentally flawed.
Continue reading
This new analysis identifies at least five areas where the final text of the EU AI Act on law enforcement use of “real time” remote biometric identification (RBI) systems in publicly accessible spaces could be improved from a fundamental rights perspective.
Continue reading
On 17 October 2023, the UK First-Tier Tribunal held the use of the surveillance system offered by the US company Clearview by non-UK law enforcement and intelligence agencies constituted “an activity which, immediately before [Brexit] completion day, fell outside the scope of EU law”, and hence the GDPR. In this brief analysis, I look at why the Tribunal came to this conclusion, and show it is fundamentally flawed.
Continue reading
I conclude that four of the five scenarios analysed by Calo et al. under US law should be criminalised under the Council of Europe’s Cybercrime Convention, but one should not.
Continue reading
Recent Comments